<?xml version="1.0" encoding="utf-8"?><feed xmlns="http://www.w3.org/2005/Atom" ><generator uri="https://jekyllrb.com/" version="4.3.4">Jekyll</generator><link href="https://jesscmoore.github.io/feed.xml" rel="self" type="application/atom+xml" /><link href="https://jesscmoore.github.io/" rel="alternate" type="text/html" /><updated>2026-09-04T11:20:27+00:00</updated><id>https://jesscmoore.github.io/feed.xml</id><title type="html">Solar powered musings</title><subtitle>Data analyst, hiker, lover of the outdoors, and once was an astronomer.</subtitle><entry><title type="html">Call for strongest possible 2035 climate target</title><link href="https://jesscmoore.github.io/2025/08/05/climate-target.html" rel="alternate" type="text/html" title="Call for strongest possible 2035 climate target" /><published>2025-08-05T03:11:02+00:00</published><updated>2025-08-05T03:11:02+00:00</updated><id>https://jesscmoore.github.io/2025/08/05/climate-target</id><content type="html" xml:base="https://jesscmoore.github.io/2025/08/05/climate-target.html"><![CDATA[<p>A brief missive that I submitted to Federal Government in the <a href="https://www.climatecouncil.org.au/actions/petition-climate-targets-and-action/?apcid=0066ea6bf4156cf29a8d2401&amp;utm_campaign=fun-bof-dc-emo-ta-lead-250&amp;utm_content=fun-bof-dc-emo-ta-lead-250&amp;utm_medium=email&amp;utm_source=ortto">petition to set the strongest possible 2035 climate target</a> in answer to Prof Tim Flannery’s callout to supporters (see the <a href="https://www.climatecouncil.org.au/">Climate Council</a>).</p>

<blockquote>
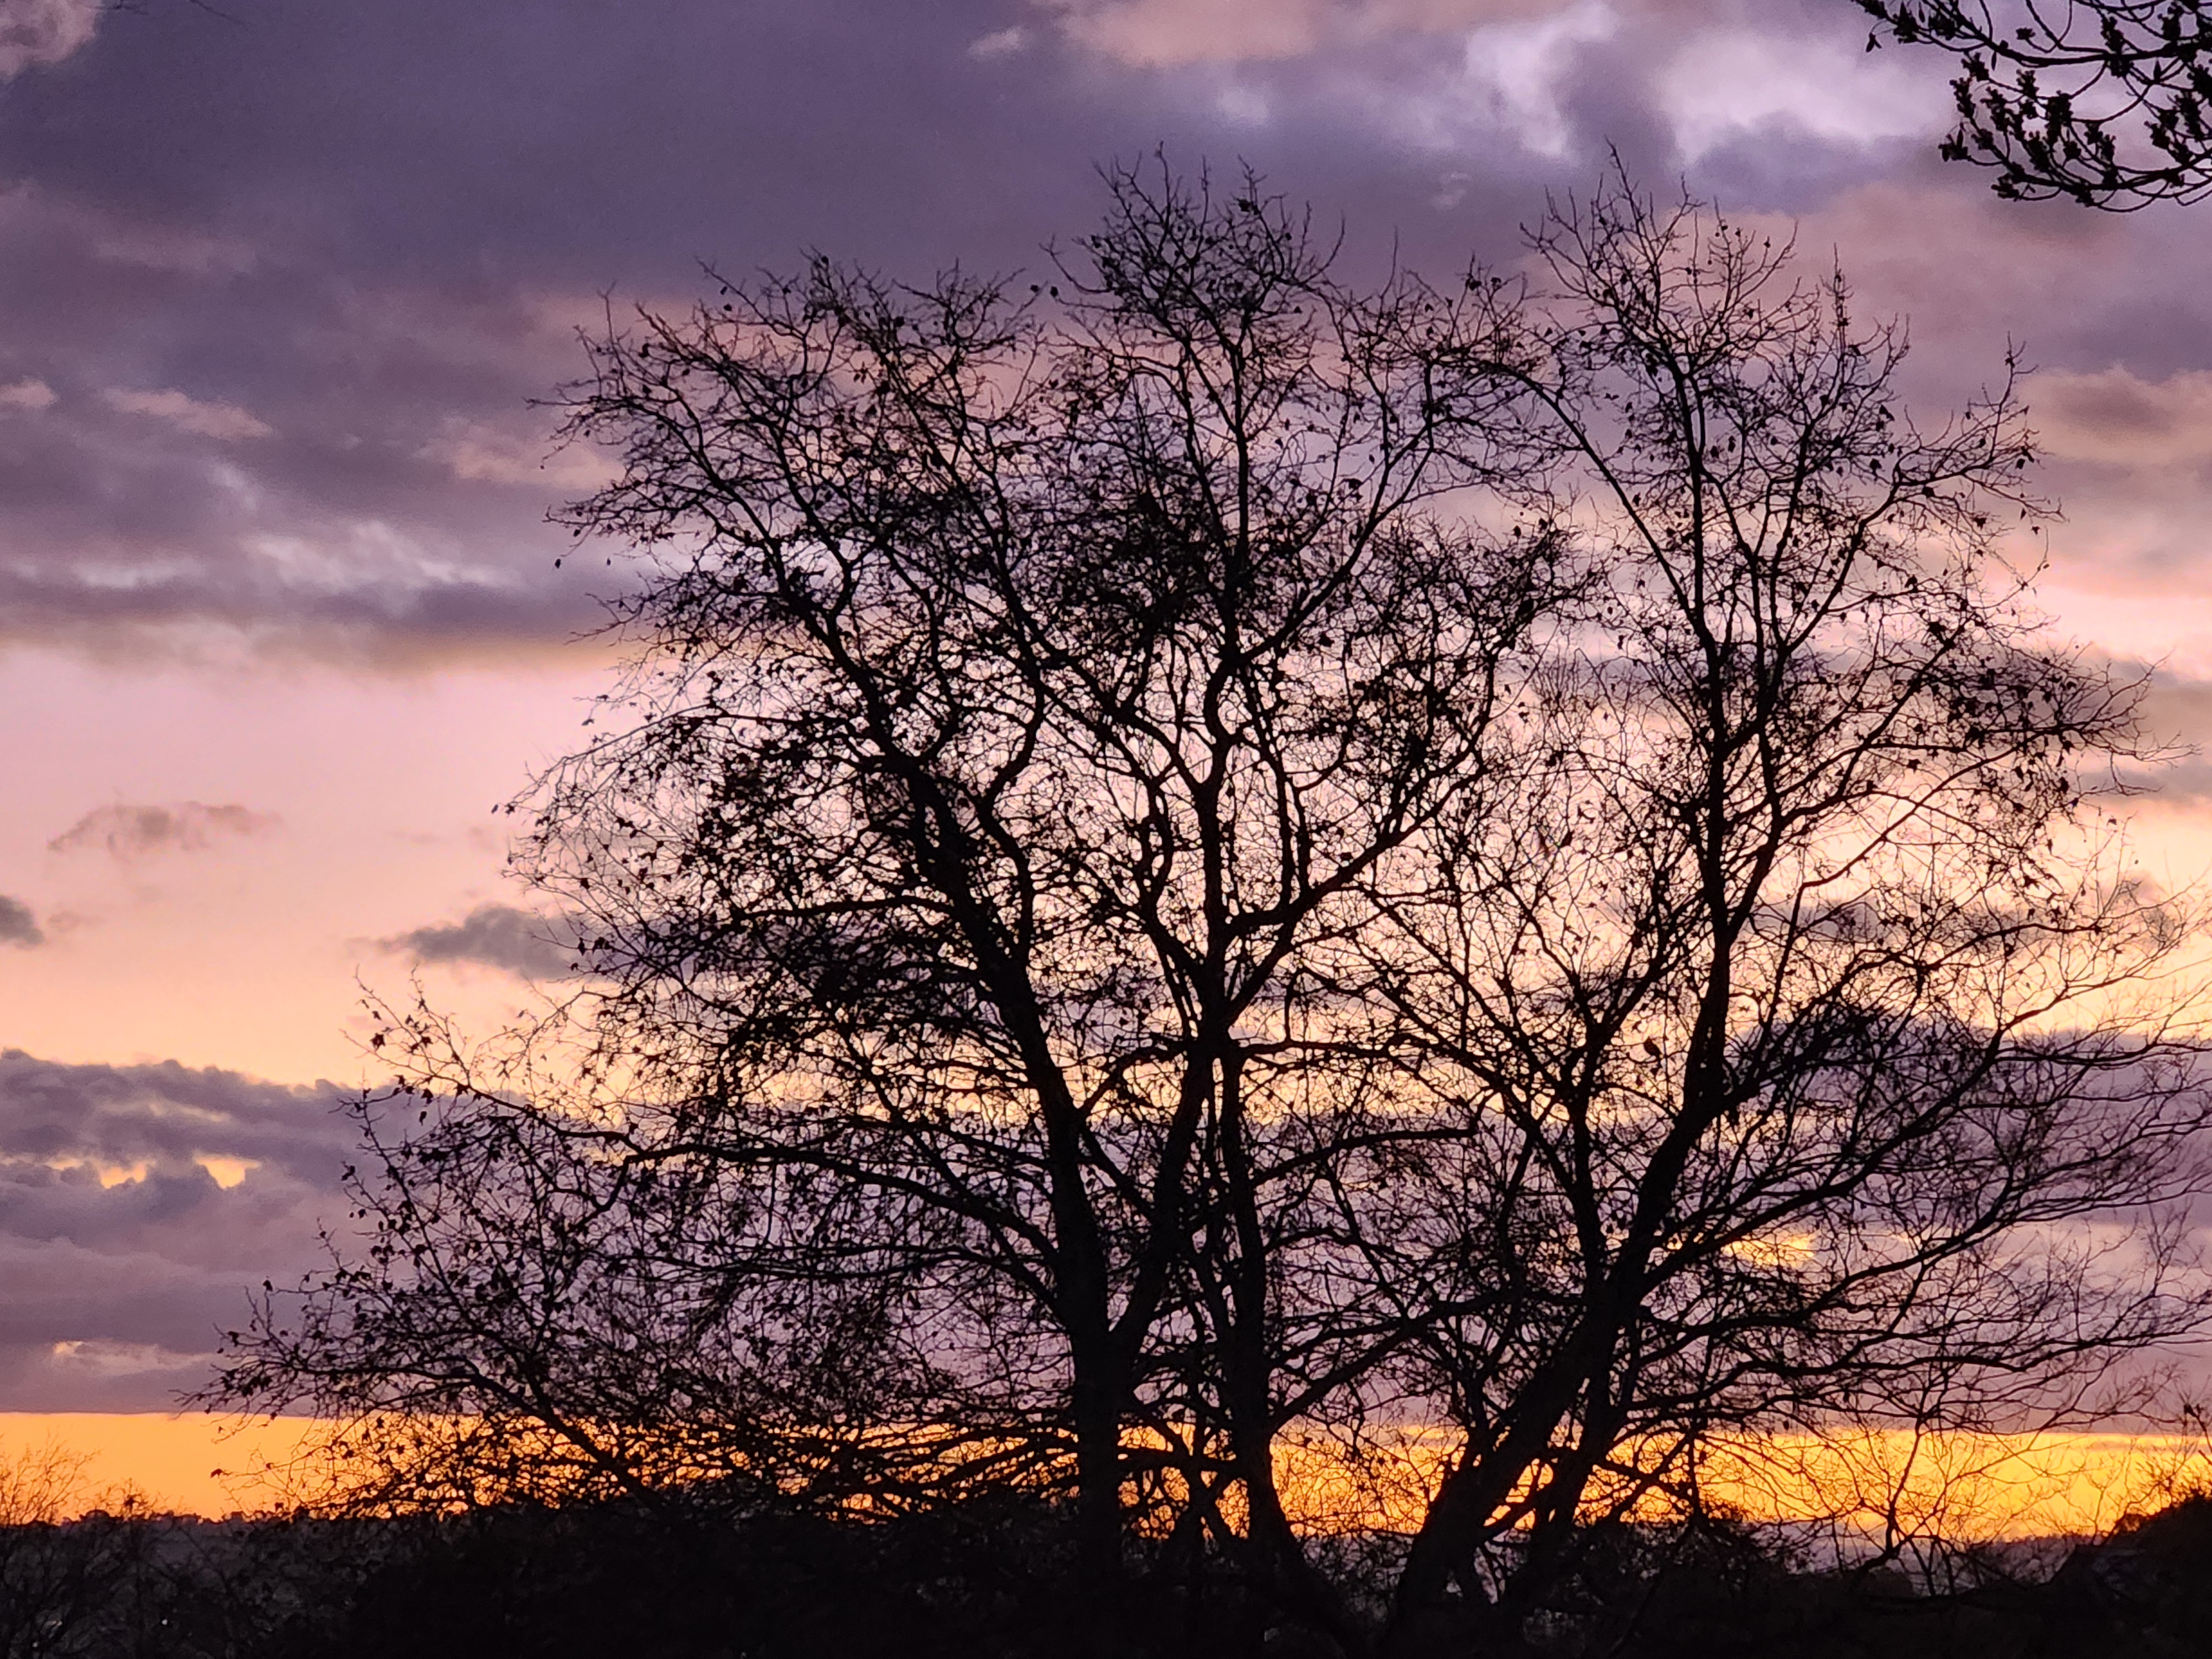
  <p>Every day that is a good day, I am nourished by Country when I take a brief time to get out for a ramble. I head up the trails any of several ways and with happy legs, 15 minutes later I’m on our local ridge.</p>

  <p>I look out at trees standing sentinel, see the horizon kiss the sky, and fellow mammals in their morning rituals. A quick nod amidst the healing breaths, and short while later I’m back peeling off falling apart runners and layers against the frost. Refreshed. Reassured that Country is still Country. Ready to get on with the day.</p>

  <p>Our land needs our care. It is doing its best to survive catastropic anthropogenic change. We must come together to collaborate, be ambitious in avoiding more disastrous environmental change. To protect our heritage and community, all the creatures in it.</p>
</blockquote>

<p><img src="https://jesscmoore.github.io/assets/images/20250805_dawnTreeChapman.jpg" alt="Dawn over a street tree near Cooleman ridge" /></p>]]></content><author><name></name></author><summary type="html"><![CDATA[A brief missive that I submitted to Federal Government in the petition to set the strongest possible 2035 climate target in answer to Prof Tim Flannery’s callout to supporters (see the Climate Council).]]></summary></entry><entry><title type="html">Allow flutter app to send and receive data</title><link href="https://jesscmoore.github.io/2025/03/05/allow_flutter_app_send_data.html" rel="alternate" type="text/html" title="Allow flutter app to send and receive data" /><published>2025-03-05T23:46:54+00:00</published><updated>2025-03-05T23:46:54+00:00</updated><id>https://jesscmoore.github.io/2025/03/05/allow_flutter_app_send_data</id><content type="html" xml:base="https://jesscmoore.github.io/2025/03/05/allow_flutter_app_send_data.html"><![CDATA[<p>Flutter app that queries an API must send and receive data by making incoming and outgoing network connections. This permission is required for apps on windows, macos, iOS and Android platforms. Apps tested on <code class="language-plaintext highlighter-rouge">Simulator</code> do not require this permission.</p>

<ul>
  <li><code class="language-plaintext highlighter-rouge">com.apple.security.network.client</code> - controls whether outgoing network connections are allowed.</li>
  <li><code class="language-plaintext highlighter-rouge">com.apple.security.network.server</code> - controls whether incoming network connections are allowed.</li>
</ul>

<p>Both must be set to <code class="language-plaintext highlighter-rouge">true</code> to allow an app to query an api and receive data.</p>

<h3 id="macos-apps">MacOS apps</h3>

<p>By default, <code class="language-plaintext highlighter-rouge">com.apple.security.network.server</code> is already set to true in debug mode entitlements file and is neither is set in the release mode entitlements file.</p>

<p>Edit <code class="language-plaintext highlighter-rouge">macos/Runner/DebugProfile.entitlements</code> and <code class="language-plaintext highlighter-rouge">macos/Runner/Release.entitlements</code> such that both are set to true with:</p>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>&lt;dict&gt;
    &lt;key&gt;com.apple.security.network.server&lt;/key&gt;
    &lt;true/&gt;
    &lt;key&gt;com.apple.security.network.client&lt;/key&gt;
    &lt;true/&gt;
&lt;/dict&gt;
</code></pre></div></div>

<p><strong>References</strong></p>

<ul>
  <li><a href="https://developer.apple.com/documentation/bundleresources/entitlements/com.apple.security.network.client">https://developer.apple.com/documentation/bundleresources/entitlements/com.apple.security.network.client</a></li>
</ul>]]></content><author><name></name></author><summary type="html"><![CDATA[Flutter app that queries an API must send and receive data by making incoming and outgoing network connections. This permission is required for apps on windows, macos, iOS and Android platforms. Apps tested on Simulator do not require this permission.]]></summary></entry><entry><title type="html">Disable Remote Management</title><link href="https://jesscmoore.github.io/2025/02/28/disable-remote-management.html" rel="alternate" type="text/html" title="Disable Remote Management" /><published>2025-02-28T11:11:17+00:00</published><updated>2025-02-28T11:11:17+00:00</updated><id>https://jesscmoore.github.io/2025/02/28/disable-remote-management</id><content type="html" xml:base="https://jesscmoore.github.io/2025/02/28/disable-remote-management.html"><![CDATA[<p>These steps are required while the newly installed MacOS is offline.</p>

<h2 id="procedure">Procedure</h2>

<h3 id="disable-system-integrity-protection">Disable System Integrity Protection</h3>

<p>Reboot into MacOS Recovery screen:</p>

<p><code class="language-plaintext highlighter-rouge">Reboot</code> &gt; Wait for blank screen &gt; Press <code class="language-plaintext highlighter-rouge">CMD+R</code></p>

<p>Open Terminal app, disable SIP and reboot to MacOS:</p>

<p>Select <code class="language-plaintext highlighter-rouge">Utilities</code> &gt; <code class="language-plaintext highlighter-rouge">Terminal</code></p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>csrutil disable
reboot
</code></pre></div></div>

<h3 id="remove-mobile-device-management">Remove Mobile Device Management</h3>

<p>From Terminal app in the MacOS Desktop, remove the Mobile Device Management profiles</p>

<p>Open <code class="language-plaintext highlighter-rouge">Terminal</code>.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo rm</span> /var/db/ConfigurationProfiles/Settings/.cloudConfigHasActivationRecord
<span class="nb">sudo rm</span> /var/db/ConfigurationProfiles/Settings/.cloudConfigRecordFound
<span class="nb">sudo touch</span> /var/db/ConfigurationProfiles/Settings/.cloudConfigProfileInstalled
<span class="nb">sudo touch</span> /var/db/ConfigurationProfiles/Settings/.cloudConfigRecordNotFound
</code></pre></div></div>

<p>Confirm they have been deleted:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo </span>profiles show <span class="nt">-type</span> enrollment
</code></pre></div></div>

<p>Stop profiles being restored:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo </span>launchctl disable system/com.apple.ManagedClient.enroll
</code></pre></div></div>

<p>Block domains used by Mac to recover MDM profiles:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>vim /etc/hosts
</code></pre></div></div>

<p>And add:</p>

<div class="language-console highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="gp">#</span><span class="w"> </span>Block MDM Remote Management
<span class="go">0.0.0.0 iprofiles.apple.com
0.0.0.0 mdmenrollment.apple.com
0.0.0.0 deviceenrollment.apple.com
0.0.0.0 gdmf.apple.com
0.0.0.0 acmdm.apple.com
0.0.0.0 albert.apple.com
</span></code></pre></div></div>

<h3 id="re-enable-system-integrity-protection">Re-enable System Integrity Protection</h3>

<p>Reboot back into Recovery system to restart SIP:</p>

<p><code class="language-plaintext highlighter-rouge">Reboot</code> &gt; Wait for blank screen &gt; Press <code class="language-plaintext highlighter-rouge">CMD+R</code></p>

<p>Open Terminal app, disable SIP and reboot to MacOS:</p>

<p>Select <code class="language-plaintext highlighter-rouge">Utilities</code> &gt; <code class="language-plaintext highlighter-rouge">Terminal</code></p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>csrutil <span class="nb">enable
</span>reboot
</code></pre></div></div>

<h3 id="reconnect-to-internet-and-update-macos">Reconnect to internet and update MacOS</h3>

<p>Back in MacOS Desktop, reconnect to internet.</p>

<p>Then confirm the system is not remotely managed with:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo </span>profiles show <span class="nt">-type</span> enrollment
</code></pre></div></div>

<p>Any MacOS updates can now be installed.</p>]]></content><author><name></name></author><summary type="html"><![CDATA[These steps are required while the newly installed MacOS is offline.]]></summary></entry><entry><title type="html">Reinstall MacOS using Installer</title><link href="https://jesscmoore.github.io/2025/02/28/macos-reinstaller.html" rel="alternate" type="text/html" title="Reinstall MacOS using Installer" /><published>2025-02-28T07:18:48+00:00</published><updated>2025-02-28T07:18:48+00:00</updated><id>https://jesscmoore.github.io/2025/02/28/macos-reinstaller</id><content type="html" xml:base="https://jesscmoore.github.io/2025/02/28/macos-reinstaller.html"><![CDATA[<p>The MacOS Install option in the MacOS Recovery screen will download a MacOS Installer for the version of MacOS that the computer was shipped with.</p>

<p>This is the the easiest option if one has a recent Mac with disabled permissions for boot from external media. As in that case it is not possible to reboot into the Startup Manager to choose an alternate boot option.</p>

<p>Select Install MacOS from the main menu in the Recovery screen and follow all the prompts.</p>

<p>Note: if you need to disable remote management, ensure the MacOS is disconnected from the internet after at the end of the install wizard process and before the computer reboots.</p>]]></content><author><name></name></author><summary type="html"><![CDATA[The MacOS Install option in the MacOS Recovery screen will download a MacOS Installer for the version of MacOS that the computer was shipped with.]]></summary></entry><entry><title type="html">Erase MacOS Operating System</title><link href="https://jesscmoore.github.io/2025/02/28/erase-macos.html" rel="alternate" type="text/html" title="Erase MacOS Operating System" /><published>2025-02-28T05:49:55+00:00</published><updated>2025-02-28T05:49:55+00:00</updated><id>https://jesscmoore.github.io/2025/02/28/erase-macos</id><content type="html" xml:base="https://jesscmoore.github.io/2025/02/28/erase-macos.html"><![CDATA[<p><strong>IMPORTANT:</strong> before erasing the MacOS operating system, make sure to turn on <a href="/2025/02/28/allow-ext-boot.html">Allow boot from external media</a>.</p>

<p>The MacOS Recovery screen has functionality to:</p>

<ul>
  <li>Delete the existing OS on hard drive in <strong>Disk Utility</strong>.</li>
  <li>View/Change startup security settings in <strong>Startup Security Utility</strong></li>
</ul>

<p>and reinstall MacOS using one of:</p>

<ul>
  <li><strong>Option 1:</strong> Download and install MacOS (requires computer online).</li>
  <li><strong>Option 2:</strong> Install MacOS from bootable external media (requires permission to boot from external media).</li>
</ul>

<p>Option 2 is preferrable as this can be the latest MacOS version, which should be downloaded and written to bootable drive before the OS is erased. Option 1 will install the MacOS version that the computer was shipped with and requires internet connection.</p>

<h2 id="procedure">Procedure</h2>

<p>Reboot into MacOS Recovery screen and choose erase your MacOS hard disk drive.</p>

<p><code class="language-plaintext highlighter-rouge">Reboot</code> &gt; Wait for blank screen &gt; Press <code class="language-plaintext highlighter-rouge">CMD+R</code></p>

<p>Open <code class="language-plaintext highlighter-rouge">Disk Utility</code> &gt; select <code class="language-plaintext highlighter-rouge">Mackintosh HD</code> volume &gt; click <code class="language-plaintext highlighter-rouge">Erase</code></p>

<p>After erasing the MacOS, reboot back to Recovery screen for next steps.</p>]]></content><author><name></name></author><summary type="html"><![CDATA[IMPORTANT: before erasing the MacOS operating system, make sure to turn on Allow boot from external media.]]></summary></entry><entry><title type="html">Allow boot from external media</title><link href="https://jesscmoore.github.io/2025/02/28/allow-ext-boot.html" rel="alternate" type="text/html" title="Allow boot from external media" /><published>2025-02-28T05:05:15+00:00</published><updated>2025-02-28T05:05:15+00:00</updated><id>https://jesscmoore.github.io/2025/02/28/allow-ext-boot</id><content type="html" xml:base="https://jesscmoore.github.io/2025/02/28/allow-ext-boot.html"><![CDATA[<p><strong>IMPORTANT: This must be done before the disk is erased as it requires a working operating system with admin user.</strong></p>

<p>Permission to allow boot from external media is set from the <strong>Startup Security Utility</strong> which is only accessible from <strong>Recovery mode</strong>:</p>

<p><code class="language-plaintext highlighter-rouge">Reboot</code> &gt; Wait for blank screen &gt; Press <code class="language-plaintext highlighter-rouge">CMD+R</code></p>

<p>Open <code class="language-plaintext highlighter-rouge">Utilities</code> &gt; <code class="language-plaintext highlighter-rouge">Startup Security Utility</code></p>

<p>Default settings are <strong>Full Security</strong> and <strong>Disallow booting from external or removable media</strong> which prevents using an external boot disk. We require no security and allow booting from external media, to allow user to boot from operating systems on external media that are not signed by Apple, such as one might need to change to a non MacOS operating system.</p>

<div class="language-console highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="go">Secure Boot: No Security
Allowed Boot Media: Allow booting from external or removable media
</span></code></pre></div></div>]]></content><author><name></name></author><summary type="html"><![CDATA[IMPORTANT: This must be done before the disk is erased as it requires a working operating system with admin user.]]></summary></entry><entry><title type="html">Setup Samba share for external drive</title><link href="https://jesscmoore.github.io/2025/02/18/samba-share-timemachine.html" rel="alternate" type="text/html" title="Setup Samba share for external drive" /><published>2025-02-18T12:57:42+00:00</published><updated>2025-02-18T12:57:42+00:00</updated><id>https://jesscmoore.github.io/2025/02/18/samba-share-timemachine</id><content type="html" xml:base="https://jesscmoore.github.io/2025/02/18/samba-share-timemachine.html"><![CDATA[<p>An external drive on Ubuntu Server can be made accessible to other machines by mounting as a Samba share drive. In this case we add the drive as a TimeMachine accessible Samba share.</p>

<p><strong>Summary</strong></p>

<ol>
  <li><code class="language-plaintext highlighter-rouge">echo -e "[my_pwd]\n[my_pwd]\n" | sudo smbpasswd -a [my_user]</code> - Add Samba user</li>
  <li><code class="language-plaintext highlighter-rouge">sudo vim /etc/samba/smb.conf</code> - Edit Samba configuration to add Timemachine readable share for external drive.</li>
  <li><code class="language-plaintext highlighter-rouge">service smbd restart</code> - Restart Samba service.</li>
  <li><code class="language-plaintext highlighter-rouge">fw allow samba</code> - Open Samba ports in firewall.</li>
  <li><code class="language-plaintext highlighter-rouge">ufw --force enable</code> - Restart firewall.</li>
</ol>

<h2 id="procedure">Procedure</h2>

<h3 id="add-samba-user">Add Samba user</h3>

<p>Add the user owning /media/[drive] as a samba user.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">echo</span> <span class="nt">-e</span> <span class="s2">"[my_pwd]</span><span class="se">\n</span><span class="s2">[my_pwd]</span><span class="se">\n</span><span class="s2">"</span> | smbpasswd <span class="nt">-a</span> <span class="o">[</span>my_user]
</code></pre></div></div>

<h3 id="add-share-to-samba-conf">Add share to Samba conf</h3>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nv">DRV_SIZE</span><span class="o">=</span>1.8T
<span class="nv">DRV_NAME</span><span class="o">=</span>seagate1-<span class="k">${</span><span class="nv">DRV_SIZE</span><span class="p">//./_</span><span class="k">}</span>
<span class="nb">cat</span> <span class="o">&gt;&gt;</span> /etc/samba/smb.conf <span class="o">&lt;&lt;</span><span class="sh">'</span><span class="no">EEOF</span><span class="sh">'

[</span><span class="k">${</span><span class="nv">DRV_NAME</span><span class="k">}</span><span class="sh">]
    comment = Backups (</span><span class="k">${</span><span class="nv">DRV_NAME</span><span class="k">}</span><span class="sh">)
    path = /media/</span><span class="k">${</span><span class="nv">DRV_NAME</span><span class="k">}</span><span class="sh">
    valid users = [my_user]
    read only = no
    vfs objects = catia fruit streams_xattr
    fruit:time machine = yes
</span><span class="no">EEOF
</span></code></pre></div></div>

<p>Confirm samba configuration with:</p>
<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">tail</span> /etc/samba/smb.conf
</code></pre></div></div>

<p>Now restart Samba daemon</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>service smbd restart
</code></pre></div></div>

<h3 id="update-firewall">Update firewall</h3>

<p>Open ports for Samba in firewall.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>ufw allow samba
ufw <span class="nt">--force</span> <span class="nb">enable</span>
</code></pre></div></div>

<p><strong>References</strong></p>

<ul>
  <li><a href="https://dev.to/ea2305/time-machine-backup-with-your-home-server-1lj6">https://dev.to/ea2305/time-machine-backup-with-your-home-server-1lj6</a></li>
  <li><a href="https://blog.jhnr.ch/2023/01/09/setup-apple-time-machine-network-drive-with-samba-on-ubuntu-22.04/">https://blog.jhnr.ch/2023/01/09/setup-apple-time-machine-network-drive-with-samba-on-ubuntu-22.04/</a></li>
</ul>]]></content><author><name></name></author><summary type="html"><![CDATA[An external drive on Ubuntu Server can be made accessible to other machines by mounting as a Samba share drive. In this case we add the drive as a TimeMachine accessible Samba share.]]></summary></entry><entry><title type="html">Mount external drives for writing MacOS files</title><link href="https://jesscmoore.github.io/2025/02/18/mount-hfsplus-drive.html" rel="alternate" type="text/html" title="Mount external drives for writing MacOS files" /><published>2025-02-18T08:28:33+00:00</published><updated>2025-02-18T08:28:33+00:00</updated><id>https://jesscmoore.github.io/2025/02/18/mount-hfsplus-drive</id><content type="html" xml:base="https://jesscmoore.github.io/2025/02/18/mount-hfsplus-drive.html"><![CDATA[<p>External drives formatted in Apple filesystems can be mounted in read write mode on Ubuntu Server OS, providing the drive is formatted in Apple HFS/HFS+ format. As of Jan 2025, there is very limited support for mounting Apple APFS formatted drives on Ubuntu, and they can only be mounted in read mode (using <a href="https://github.com/sgan81/apfs-fuse">https://github.com/sgan81/apfs-fuse</a> library)</p>

<p><strong>Summary</strong></p>

<ol>
  <li><code class="language-plaintext highlighter-rouge">apt-get install hfsprogs</code> - Install <code class="language-plaintext highlighter-rouge">hfsprogs</code> package required to read-write to drives with file format HFS/HFS+</li>
  <li><code class="language-plaintext highlighter-rouge">sudo fdisk -l</code> - fetch device block name and file type of externam drive.</li>
  <li><code class="language-plaintext highlighter-rouge">mkdir -p /media/[mount_name]</code> - create mount point.</li>
  <li><code class="language-plaintext highlighter-rouge">sudo mount -v -t hfsplus -o force,rw,uid=1000,gid=1000 [device_vol_name] /media/[mount_name]</code>- mount the device volume at mount point.</li>
  <li><code class="language-plaintext highlighter-rouge">sudo blkid [device_vol_name] | awk -F'"' '{print $2}'</code> - fetch device volume block id to use in <code class="language-plaintext highlighter-rouge">/etc/fstab</code>.</li>
  <li><code class="language-plaintext highlighter-rouge">sed -i '\$a '"UUID=[device_block_id] /media/[mount_name] hfsplus nosuid,nodev,nofail,force,rw,uid=1000,gid=1000 0 0" /etc/fstab</code> - add device volume mounting to <code class="language-plaintext highlighter-rouge">/etc/fstab</code>.</li>
</ol>

<h2 id="procedure">Procedure</h2>

<h3 id="install-hfsprogs">Install hfsprogs</h3>

<p>Package <code class="language-plaintext highlighter-rouge">hfsprogs</code> is required to force rw mounting of HFS+ file systems.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>apt-get update
apt-get <span class="nb">install </span>hfsprogs
</code></pre></div></div>

<h3 id="identify-device-volume">Identify device volume</h3>

<p>First, fetch the volume block details of the external drive. We do this by searching for Apple type devices excluding Apple boot devices.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo </span>fdisk <span class="nt">-l</span> | <span class="nb">grep </span>Apple | <span class="nb">grep</span> <span class="nt">-iv</span> <span class="s1">'Apple boot'</span>
</code></pre></div></div>

<p>If you have multiple Apple formatted external drives, identify the drive  volume of interest from volume size. In our case we see that the drive size is 1.8T, and use that to fetch the volume name, which is the first argument returned.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nv">DRV_SIZE</span><span class="o">=</span>1.8T
<span class="nv">BLK</span><span class="o">=</span><span class="s2">"</span><span class="si">$(</span><span class="nb">sudo </span>fdisk <span class="nt">-l</span> | <span class="nb">grep </span>Apple | <span class="nb">grep</span> <span class="nt">-iv</span> <span class="s1">'Apple boot'</span> | <span class="nb">grep</span> <span class="nv">$DRV_SIZE</span><span class="si">)</span><span class="s2">"</span>
<span class="nv">BLK_NAME</span><span class="o">=</span><span class="s2">"</span><span class="si">$(</span><span class="nb">echo</span> <span class="k">${</span><span class="nv">BLK</span><span class="k">}</span> | <span class="nb">awk</span> <span class="s1">'{print $1}'</span><span class="si">)</span><span class="s2">"</span>
</code></pre></div></div>

<p><code class="language-plaintext highlighter-rouge">fdisk -l</code> also shows that the volume is type “Apple HFS/HFS+” which we can mount as type “hfsplus”. If the drive is Apple APFS format, it cannot be mounted read write on Ubuntu, and will need to be erased and reformatted as Apple HFS/HFS+ format using Disk Utility app or <code class="language-plaintext highlighter-rouge">diskutil</code> on MacOS machine.</p>

<h3 id="mount-hfs">Mount HFS</h3>

<p>Next, create the directory that will be the mount point. On Ubuntu Server, external drives are mounted in /media. To associate the mount directory with the drive, we append the drive size to the drive name(replacing full stops with underscores).</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nv">DRV_NAME</span><span class="o">=</span>seagate1-<span class="k">${</span><span class="nv">DRV_SIZE</span><span class="p">//./_</span><span class="k">}</span>
<span class="nb">mkdir</span> <span class="nt">-p</span> /media/<span class="k">${</span><span class="nv">DRV_NAME</span><span class="k">}</span>
</code></pre></div></div>

<p>Mount the device volume using <code class="language-plaintext highlighter-rouge">-v</code> for verbose, and <code class="language-plaintext highlighter-rouge">force, rw</code> to force mounting in read-write mode. User and Group permissions of the mount directory should be set to <code class="language-plaintext highlighter-rouge">uid=1000,gid=1000</code> to set the primary account holder as user and group owner. The file system type is <code class="language-plaintext highlighter-rouge">hfsplus</code>.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo </span>mount <span class="nt">-v</span> <span class="nt">-t</span> hfsplus <span class="nt">-o</span> force,rw,uid<span class="o">=</span>1000,gid<span class="o">=</span>1000 <span class="k">${</span><span class="nv">BLK_NAME</span><span class="k">}</span> /media/<span class="k">${</span><span class="nv">DRV_NAME</span><span class="k">}</span>
</code></pre></div></div>

<p>Confirm the drive is mounted with <code class="language-plaintext highlighter-rouge">mount -l</code> or <code class="language-plaintext highlighter-rouge">ls -l /media</code></p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>mount <span class="nt">-l</span> |grep <span class="nt">-i</span> <span class="k">${</span><span class="nv">DRV_NAME</span><span class="k">}</span>
<span class="nb">ls</span> <span class="nt">-l</span> /media
</code></pre></div></div>

<h3 id="add-drive-to-etcfstab">Add drive to /etc/fstab</h3>

<p>The mount rule needs to be added to <code class="language-plaintext highlighter-rouge">/etc/fstab</code> in order to mount the drive on reboot. The fstab file uses the block id to identify the device volume which we fetch with <code class="language-plaintext highlighter-rouge">blkid</code> which returns the block id as the second argument.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nv">BLK_ID</span><span class="o">=</span><span class="s2">"</span><span class="si">$(</span><span class="nb">sudo </span>blkid <span class="k">${</span><span class="nv">BLK_NAME</span><span class="k">}</span> | <span class="nb">awk</span> <span class="nt">-F</span><span class="s1">'"'</span> <span class="s1">'{print $2}'</span><span class="si">)</span><span class="s2">"</span>
<span class="nv">FSTAB_RULE</span><span class="o">=</span><span class="s2">"UUID=</span><span class="k">${</span><span class="nv">BLK_ID</span><span class="k">}</span><span class="s2"> /media/</span><span class="k">${</span><span class="nv">DRV_NAME</span><span class="k">}</span><span class="s2"> hfsplus nosuid,nodev,nofail,force,rw,uid=1000,gid=1000 0 0"</span>
<span class="nb">sed</span> <span class="nt">-i</span> <span class="s1">'\$a '</span><span class="s2">"</span><span class="k">${</span><span class="nv">FSTAB_RULE</span><span class="k">}</span><span class="s2">"</span> /etc/fstab
</code></pre></div></div>

<p>Confirm the drive is added with:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">cat</span> /etc/fstab
</code></pre></div></div>

<p>Note: the drive does not automount when plugged into Ubuntu Server machine. The user needs to run <code class="language-plaintext highlighter-rouge">mount ....</code> to mount it.</p>

<h2 id="troubleshooting">Troubleshooting</h2>

<p>The drive may mount as readonly (<code class="language-plaintext highlighter-rouge">ro</code>), despite options <code class="language-plaintext highlighter-rouge">force, rw</code> in the mount command. This is detected as:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>mount <span class="nt">-l</span> |grep /media
/dev/sdb2 on /media/seagate1-1_8T <span class="nb">type </span>hfsplus <span class="o">(</span>ro,relatime,umask<span class="o">=</span>22,uid<span class="o">=</span>1000,gid<span class="o">=</span>1000,nls<span class="o">=</span>utf8<span class="o">)</span>
</code></pre></div></div>

<p>Review <code class="language-plaintext highlighter-rouge">dmesg</code>:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo </span>dmesg | <span class="nb">grep </span>hfsplus | more
hfsplus: Filesystem was not cleanly unmounted, running fsck.hfsplus is recommended.  mounti
ng read-only.
</code></pre></div></div>

<p>Running <code class="language-plaintext highlighter-rouge">fsck.hfsplus</code> on the drive fixed the issue, after which re-running mount  correctly mounted the drive in <code class="language-plaintext highlighter-rouge">rw</code> mode.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">sudo </span>fsck.hfsplus /dev/sdb2
</code></pre></div></div>

<p>Then unmount and remount disk. If not unmounting, ensure the mount point is not in use, navigate elsewhere, then use lazy unmount and forced umount if necessaary. If unmounted and still failing to umount due to ‘already mounted or mount point busy’ error, then <code class="language-plaintext highlighter-rouge">reboot</code> can be the easiest option to remount the disk.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">cd
sudo </span>umount <span class="nt">-l</span> /dev/sdb2
<span class="nb">sudo </span>umount <span class="nt">-f</span> /dev/sdb2
</code></pre></div></div>]]></content><author><name></name></author><summary type="html"><![CDATA[External drives formatted in Apple filesystems can be mounted in read write mode on Ubuntu Server OS, providing the drive is formatted in Apple HFS/HFS+ format. As of Jan 2025, there is very limited support for mounting Apple APFS formatted drives on Ubuntu, and they can only be mounted in read mode (using https://github.com/sgan81/apfs-fuse library)]]></summary></entry><entry><title type="html">Remove remote management from MacOS</title><link href="https://jesscmoore.github.io/2025/02/14/MacOS-remove-remote-management.html" rel="alternate" type="text/html" title="Remove remote management from MacOS" /><published>2025-02-14T10:11:11+00:00</published><updated>2025-02-14T10:11:11+00:00</updated><id>https://jesscmoore.github.io/2025/02/14/MacOS-remove-remote-management</id><content type="html" xml:base="https://jesscmoore.github.io/2025/02/14/MacOS-remove-remote-management.html"><![CDATA[<p>Removing remote management requires erasing the MacOS installation and unsetting the external Mobile Device Management profile (MDM) during a fresh installation. The computer is temporarily disconnected from the internet to prevent reinstall of the MDM profile.</p>

<p>Permission to boot from external disk is disabled by default in recent MacOS (since ~2020). To enable install from bootable USB, this setting must be enabled from recovery mode <strong>before the operating system is deleted</strong> (while the user exists with admin permissions).</p>

<h2 id="procedure">Procedure</h2>

<h3 id="download-macos"><a href="/2025/02/14/download_macos_installer.html">Download MacOS</a></h3>

<h3 id="burn-macos-onto-a-bootable-usb-drive"><a href="/2025/02/14/create-macos-boot-disk.html">Burn MacOS onto a bootable USB drive</a></h3>

<h3 id="allow-boot-from-external-media"><a href="/2025/02/28/allow-ext-boot.html">Allow boot from external media</a></h3>

<h3 id="erase-existing-macos"><a href="/2025/02/28/erase-macos.html">Erase existing MacOS</a></h3>

<hr />

<h3 id="install-macos-using-recovery-installer"><a href="/2025/02/28/macos-reinstaller.html">Install MacOS using Recovery Installer</a></h3>

<p>or</p>

<h3 id="install-macos-from-bootable-external-media"><a href="/2025/02/14/install-macOS-from-disk.html">Install MacOS from bootable external media</a></h3>

<hr />

<h3 id="disable-remote-management"><a href="/2025/02/28/disable-remote-management.html">Disable Remote Management</a></h3>

<p><strong>References</strong></p>

<ul>
  <li><a href="https://williamhartz.medium.com/how-to-remove-remote-management-screen-from-macbook-without-password-2023-486ac1476acc">https://williamhartz.medium.com/how-to-remove-remote-management-screen-from-macbook-without-password-2023-486ac1476acc</a></li>
  <li><a href="https://medium.com/@perbcreate/how-to-remove-remote-management-mdm-from-m1-macbook-without-a-password-983a8f93427a">https://medium.com/@perbcreate/how-to-remove-remote-management-mdm-from-m1-macbook-without-a-password-983a8f93427a</a></li>
  <li><a href="https://github.com/assafdori/bypass-mdm">https://github.com/assafdori/bypass-mdm</a></li>
  <li><a href="https://support.apple.com/en-au/102603">https://support.apple.com/en-au/102603</a> - MacOS Startup key combinations</li>
</ul>]]></content><author><name></name></author><summary type="html"><![CDATA[Removing remote management requires erasing the MacOS installation and unsetting the external Mobile Device Management profile (MDM) during a fresh installation. The computer is temporarily disconnected from the internet to prevent reinstall of the MDM profile.]]></summary></entry><entry><title type="html">Install MacOS from Bootable Disk</title><link href="https://jesscmoore.github.io/2025/02/14/install-macOS-from-disk.html" rel="alternate" type="text/html" title="Install MacOS from Bootable Disk" /><published>2025-02-14T08:26:41+00:00</published><updated>2025-02-14T08:26:41+00:00</updated><id>https://jesscmoore.github.io/2025/02/14/install-macOS-from-disk</id><content type="html" xml:base="https://jesscmoore.github.io/2025/02/14/install-macOS-from-disk.html"><![CDATA[<p>Booting from disk will only be possible on more recent Macs if Startup Security Utility settings have enabled <strong>Allow boot from External Media</strong>.</p>

<h2 id="procedure">Procedure</h2>

<p>Power off the Mac.</p>

<p>Insert the bootable installer disk.</p>

<p>Access the Startup (boot) menu by:</p>

<p>Press <code class="language-plaintext highlighter-rouge">Power</code> + <code class="language-plaintext highlighter-rouge">Option</code> keys.</p>

<p>Select the bootable installer, then click <code class="language-plaintext highlighter-rouge">Continue</code> to start the Installer wizard and follow the installation steps</p>

<p>If needing to disable remote management, ensure you disconnect from internet before the last 1-2 minutes of the end of the install routine. Connecting to internet via mobile hotspot is an easy network option, as the computer can be quickly disconnected from the net by turning off the hotspot.</p>

<h2 id="troubleshooting">Troubleshooting</h2>

<p>Alternatively, if the bootable USB drive is mounted, OS install wizard can be initiated by running <code class="language-plaintext highlighter-rouge">startosinstall</code> on the Volume from the Recovery screen. However, this will only be possible if the startup security settings have enabled allow boot from external media.</p>

<p>Access the Recovery screen menu by:</p>

<p>Press <code class="language-plaintext highlighter-rouge">Power</code>. Then press <code class="language-plaintext highlighter-rouge">CMD</code> + <code class="language-plaintext highlighter-rouge">R</code>/</p>

<p>Open <code class="language-plaintext highlighter-rouge">Utilities</code> menu &gt; select <code class="language-plaintext highlighter-rouge">Terminal</code>:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">cd</span> /Volumes/Install<span class="se">\ </span>macOS<span class="se">\ </span>Sequoia.app/Contents/Resources/startosinstall
</code></pre></div></div>

<p>For options use:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>...path/to/startosinstall <span class="nt">--usage</span>
</code></pre></div></div>

<p><strong>References</strong></p>

<ul>
  <li><a href="">https://support.apple.com/en-us/101578</a> - Use the bootable installer</li>
  <li><a href="https://support.apple.com/en-au/guide/mac-help/mchlp1034/mac">https://support.apple.com/en-au/guide/mac-help/mchlp1034/mac</a> - Change your Mac startup disk</li>
</ul>]]></content><author><name></name></author><summary type="html"><![CDATA[Booting from disk will only be possible on more recent Macs if Startup Security Utility settings have enabled Allow boot from External Media.]]></summary></entry></feed>